Licensable IP
K1 — secp256k1 compute engine
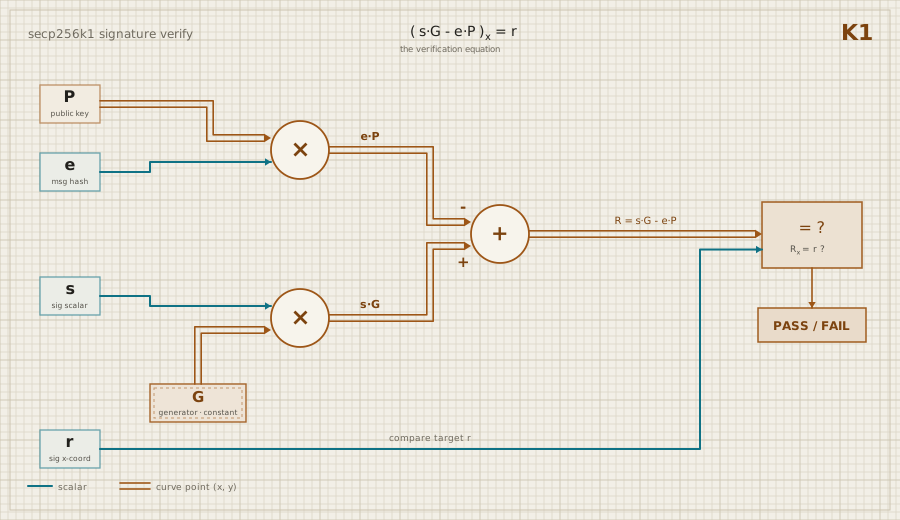
K1 accelerates the compute-heavy elliptic-curve arithmetic of secp256k1 — the curve behind Bitcoin and many major cryptocurrencies. Its flagship measured workload is Schnorr signature verification. The architecture is licensable IP; integration details are available under NDA.
Throughput scales with cores
Efinix Ti375 (Titanium) FPGA · C4 model · 2026-07-24K1 is instantiated per core, and the engine is simply as many cores as the fabric holds. Pick a core count to see the static-timing throughput ceiling, the per-verification latency, and the FPGA resources it takes. The four-core engine's ceiling is 307,800 verifications/s; in the Blitz card the host measures 297,100/s sustained end to end — the gap is real-world DMA and windowing overhead.
The build on Efinix Ti375 (Titanium) — 4 cores
resources from build reportOn FPGA each core closes well short of that 1 GHz clock-tree ceiling. We expect an ASIC implementation of the same architecture to close at a much higher clock — and so run substantially faster for the same design. We will publish measured ASIC figures the same way once we have them.
Verification, shown
Every figure below is generated from our repositories — the same test suites, formal proofs, and build reports that gate our own commits — and carries the commit it came from. Where the work is public, you can check it: the known-answer corpus is downloadable below, and an open-source verification core is on our GitLab to run it against.
last assembled 2026-09-18 · reassembled nightly
How much of the chip's source code our test suites actually exercise. Untested lines are where bugs hide — this measures how few places they have left.
1,410/1,544 lines across 34 RTL files (Verilator line coverage, tested configs)
k1@fe49068 coverage_report · 2026-09-18
Automated testbenches that check every module's behavior against a reference model, run on every change — the design can't move forward while any of them fail.
module testbenches, full suite — 42 passed, 0 failed
k1@fe49068 run_tests.sh · 2026-09-18
Mathematical proofs, not tests: a solver shows certain failures are impossible for every input, not just the ones we tried. Each proof is paired with a check that it can't pass emptily.
14 bound proofs + 6 anti-vacuity checks. SymbiYosys proofs over the arithmetic cones; every safe bound is paired with a must-fail tighter bound so no proof can pass vacuously.
k1@5216245 fv/RESULTS.json · 2026-08-07
Tricky inputs with independently computed correct answers — including deliberately invalid signatures the hardware must reject. The chip's verdicts match the reference implementation on every one.
18 boundary vectors, plus a 1,042-vector cosimulation corpus.
blitz@21cf508 rtl/cores/open/sim/kat_corpus.txt · 2026-09-18
A fuzzer runs against this exact build around the clock: freshly signed signatures cross-checked against the reference software implementation, plus adversarially mutated must-fail twins hunting specifically for a wrong PASS — the failure mode that matters. The counter resets whenever the build changes.
96,801,800 cross-checked, 0 mismatches; 387,207,200/387,207,200 must-fail twins rejected. Build 22f7ecd2, since 2026-08-07.
blitz-fuzz tracker (continuous, bench-local state) · 2026-09-18
Small faults deliberately planted in the synthesized logic — an inverted condition, a stuck bit — each of which the test suite must catch. A surviving mutant is logic the tests execute but never actually check; line coverage alone cannot see the difference.
92.6% caught across 7 module rigs.
k1@72e402a mcy/RESULTS.json · 2026-08-07
The corpus is open — check it yourself
Our known-answer corpus is fully open: adversarial boundary cases with verdicts derived from the reference implementation. Run the vectors against your own secp256k1 code, cross-check them however you like, or run them through our open-source verification core and watch it produce the same answers.
The scheme is the Nexa/BCH Schnorr variant (not BIP-340); the exact accept/reject rules are the corpus itself.
Or run the whole suite against our open core
A working, MIT-licensed verification core — simulation testbenches, the KAT corpus, and a cosimulation harness included. Two commands, no hardware required (needs Verilator):
git clone https://git.nodelabs.ca/blitz/blitz_opencore.git
cd blitz_opencore/sim && ./run_tests.sh
Tested cold from a fresh anonymous clone, 2026-08-16 — exactly the two commands above: lint, KAT corpus, ROM provenance, microcode difftest, engine lockstep in three configs, and a 50-vector cosimulation — ALL TESTS PASSED.
License K1
K1 runs today inside the Blitz accelerator card and is available for licensing. Architecture details, integration documentation, and evaluation access are provided under NDA.
Start the conversation